


Certification Topics of XK0-005 Exam PDF Recently Updated Questions
XK0-005 Exam Prep Guide: Prep guide for the XK0-005 Exam
CompTIA XK0-005 exam is a certification that evaluates the skills of professionals in working with Linux-based systems. CompTIA Linux+ Certification Exam certification is useful for both newcomers and professionals working in the IT or Linux administration domains. CompTIA Linux+ Certification Exam certification is vendor-neutral, which means that it recognizes skills regardless of a candidate's Linux distribution, opening the way for a broader pool of candidates. Passing XK0-005 exam can help professionals distinguish themselves in the job market and demonstrate critical thinking, independent operating, and complex problem-solving abilities.
NEW QUESTION # 143
A developer reported an incident involving the application configuration file /etc/httpd/conf/httpd.conf that is missing from the server. Which of the following identifies the RPM package that installed the configuration file?
- A. rpm -qf /etc/httpd/conf/httpd.conf
- B. rpm -query /etc/httpd/conf/httpd.conf
- C. rpm -q /etc/httpd/conf/httpd.conf
- D. rpm -ql /etc/httpd/conf/httpd.conf
Answer: D
NEW QUESTION # 144
A Linux administrator is troubleshooting the root cause of a high CPU load and average.
Which of the following commands will permanently resolve the issue?
- A. iostat -cy 1 5
- B. renice -n -20 6295
- C. kill -9 6295
- D. pstree -p 6295
Answer: C
Explanation:
Explanation
The command that will permanently resolve the issue of high CPU load and average is kill -9 6295. This command will send a SIGKILL signal to the process with the PID 6295, which is the process that is consuming 99.7% of the CPU according to the top output. The SIGKILL signal will terminate the process immediately and free up the CPU resources. The kill command is used to send signals to processes by PID or name.
The other options are not correct commands for resolving this issue. The renice -n -20 6295 command will change the priority (niceness) of the process with PID 6295 to -20, which is the highest priority possible. This will make the process more CPU-intensive, not less. The renice command is used to change the priority of running processes. The pstree -p 6295 command will show a tree of processes with PID 6295 as the root. This will not affect the CPU load or average, but only display information. The pstree command is used to display a tree of processes. The iostat -cy 1 5 command will show CPU and disk I/O statistics for 5 iterations with an interval of 1 second. This will also not affect the CPU load or average, but only display information. The iostat command is used to report CPU and I/O statistics. References: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 11: Troubleshooting Linux Systems; kill(1) - Linux manual page; renice(1) - Linux manual page; pstree(1) - Linux manual page; iostat(1) - Linux manual page
NEW QUESTION # 145
When trying to log in remotely to a server, a user receives the following message: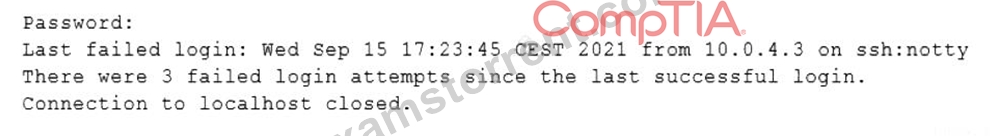
The server administrator is investigating the issue on the server and receives the following outputs:
Which of the following is causing the issue?
- A. The account was locked out due to three failed logins.
- B. The user entered the wrong password.
- C. The wrong permissions are on the user's home directory.
- D. The user has the wrong shell assigned to the account.
Answer: D
Explanation:
The user has the wrong shell assigned to the account, which is causing the issue. The output 1 shows that the user's shell is set to /bin/false, which is not a valid shell and will prevent the user from logging in. The output 2 shows that the user's home directory has the correct permissions (drwxr-xr-x), and the output 3 shows that the user entered the correct password and was accepted by the SSH daemon, but the session was closed immediately due to the invalid shell. The other options are incorrect because they are not supported by the outputs. Reference: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 13: Managing Network Services, page 413.
NEW QUESTION # 146
Due to performance issues on a server, a Linux administrator needs to termi-nate an unresponsive process.
Which of the following commands should the
administrator use to terminate the process immediately without waiting for a graceful shutdown?
- A. kill -SIGTERM 5545
- B. kill -SIGKILL 5545
- C. kill -SIGINT 5545
- D. kill -SIGHUP 5545
Answer: B
Explanation:
To terminate an unresponsive process immediately without waiting for a graceful shutdown, the administrator can use the command kill -SIGKILL 5545 (A). This will send a signal to the process with the PID 5545 that cannot be ignored or handled by the process, and force it to stop. The other commands will send different signals that may allow the process to perform some cleanup or termination actions, or may be ignored by the process. References:
* [CompTIA Linux+ Study Guide], Chapter 6: Managing Processes, Section: Killing Processes
* [How to Kill Processes in Linux]
NEW QUESTION # 147
A systems administrator wants to upgrade /bin/someapp to a new version, but the administrator does not know the package name. Which of the following will show the RPM package name that provides that binary file?
- A. rpm -Vv /bin/someapp
- B. rpm -qf /bin/someapp
- C. rpm -i /bin/someapp
- D. rpm -p /bin/someapp
Answer: B
Explanation:
Use the command 'rpm -qf' or 'yum whatprovides' to get the package name from a binary file or library file on the server.
NEW QUESTION # 148
An administrator needs to make an application change via a script that must be run only in console mode. Which of the following best represents the sequence the administrator should execute to accomplish this task?
- A. systemctl isolate multi-user.target
sh script.sh
systemctl isolate graphical.target - B. systemctl isolate multi-user.target
systemctl isolate graphical.target
sh script.sh - C. sh script.sh
systemctl isolate multi-user.target
systemctl isolate graphical.target - D. systemctl isolate graphical.target
sh script.sh
systemctl isolate multi-user.target
Answer: A
Explanation:
This sequence will allow the administrator to switch from the graphical mode to the console mode, run the script, and then switch back to the graphical mode. The systemctl command is used to control the systemd system and service manager, which manages the boot targets and services on Linux systems. The isolate subcommand starts the unit specified on the command line and its dependencies and stops all others. The multi-user.target is a boot target that provides a text-based console login, while the graphical.target is a boot target that provides a graphical user interface. By using systemctl isolate, the administrator can change the boot target on the fly without rebooting the system.
The sh command is used to run a shell script, which is a file that contains a series of commands that can be executed by the shell. The script.sh is the name of the script that contains the application change that the administrator needs to make. By running sh script.sh, the administrator can execute the script in the console mode.
NEW QUESTION # 149
A development team asks an engineer to guarantee the persistency of journal log files across system reboots.
Which of the following commands would accomplish this task?
- A. cat /etc/systemd/journald.conf | awk '(print $1,$3)'
- B. journalctl --list-boots && systemctl restart systemd-journald.service
- C. grep -i auto /etc/systemd/journald.conf && systemctl restart systemd-journald.service
- D. sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q'
/etc/systemd/journald.conf
Answer: D
Explanation:
Explanation
The command sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q'
/etc/systemd/journald.conf will accomplish the task of guaranteeing the persistency of journal log files across system reboots. The sed command is a tool for editing text files on Linux systems. The -i option modifies the file in place. The s command substitutes one string for another. The g flag replaces all occurrences of the string. The && operator executes the second command only if the first command succeeds. The q command quits after the first match. The /etc/systemd/journald.conf file is a configuration file for the systemd-journald service, which is responsible for collecting and storing log messages. The command sed -i 's/auto/persistent/g'
/etc/systemd/journald.conf will replace the word auto with the word persistent in the file. This will change the value of the Storage option, which controls where the journal log files are stored. The value auto means that the journal log files are stored in the volatile memory and are lost after reboot, while the value persistent means that the journal log files are stored in the persistent storage and are preserved across reboots. The command sed -i 'persistent/s/'#//q' /etc/systemd/journald.conf will remove the # character at the beginning of the line that contains the word persistent. This will uncomment the Storage option and enable it.
The command sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q'
/etc/systemd/journald.conf will guarantee the persistency of journal log files across system reboots by changing and enabling the Storage option to persistent. This is the correct command to use to accomplish the task. The other options are incorrect because they either do not change the value of the Storage option (grep -i auto /etc/systemd/journald.conf && systemctl restart systemd-journald.service or cat
/etc/systemd/journald.conf | awk '(print $1,$3)') or do not enable the Storage option (journalctl --list-boots && systemctl restart systemd-journald.service). References: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 16: Managing Logging and Monitoring, page 489.
NEW QUESTION # 150
A Linux administrator is updating the file that contains the addresses of the software and update repositories on an Ubuntu system. Which of the following files needs to be edited to accomplish this task?
- A. /etc/apt/sources.list
- B. /etc/dnf/dnf.conf
- C. /etc/yum/yum.conf
- D. /etc/apt/listchanges.conf
Answer: A
NEW QUESTION # 151
A DevOps engineer is working on a local copy of a Git repository. The engineer would like to switch from the main branch to the staging branch but notices the staging branch does not exist.
Which of the following Git commands should the engineer use to perform this task?
- A. git status --b staging
- B. git commit --m staging
- C. git branch --m staging
- D. git checkout --b staging
Answer: D
Explanation:
This command will create a new branch named staging and switch to it. The git checkout command is used to switch between branches or restore files from a specific branch. The -b option is used to create a new branch if it does not exist. For example, git checkout -b staging will create and switch to the staging branch.
NEW QUESTION # 152
A development team asks an engineer to guarantee the persistency of journal log files across system reboots. Which of the following commands would accomplish this task?
- A. sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q' /etc/systemd/journald.conf
- B. cat /etc/systemd/journald.conf | awk '(print $1,$3)'
- C. journalctl --list-boots && systemctl restart systemd-journald.service
- D. grep -i auto /etc/systemd/journald.conf && systemctl restart systemd-journald.service
Answer: A
Explanation:
The command sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q' /etc/systemd/journald.conf will accomplish the task of guaranteeing the persistency of journal log files across system reboots. The sed command is a tool for editing text files on Linux systems. The -i option modifies the file in place. The s command substitutes one string for another. The g flag replaces all occurrences of the string. The && operator executes the second command only if the first command succeeds. The q command quits after the first match. The /etc/systemd/journald.conf file is a configuration file for the systemd-journald service, which is responsible for collecting and storing log messages. The command sed -i 's/auto/persistent/g' /etc/systemd/journald.conf will replace the word auto with the word persistent in the file. This will change the value of the Storage option, which controls where the journal log files are stored. The value auto means that the journal log files are stored in the volatile memory and are lost after reboot, while the value persistent means that the journal log files are stored in the persistent storage and are preserved across reboots. The command sed -i 'persistent/s/'#//q' /etc/systemd/journald.conf will remove the # character at the beginning of the line that contains the word persistent. This will uncomment the Storage option and enable it. The command sed -i 's/auto/persistent/g' /etc/systemd/journald.conf && sed -i 'persistent/s/'#//q' /etc/systemd/journald.conf will guarantee the persistency of journal log files across system reboots by changing and enabling the Storage option to persistent. This is the correct command to use to accomplish the task. The other options are incorrect because they either do not change the value of the Storage option (grep -i auto /etc/systemd/journald.conf && systemctl restart systemd-journald.service or cat /etc/systemd/journald.conf | awk '(print $1,$3)') or do not enable the Storage option (journalctl --list-boots && systemctl restart systemd-journald.service). Reference: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 16: Managing Logging and Monitoring, page 489.
NEW QUESTION # 153
Following the migration from a disaster recovery site, a systems administrator wants a server to require a user to change credentials at initial login. Which of the following commands should be used to ensure the aging attribute?
- A. chage -E 0 user
- B. chage -d 0 user
- C. chage -d 1 user
- D. chage -d 2 user
Answer: B
Explanation:
Explanation
The chage command can be used to change the user password expiry information. The -d or --lastday option sets the last password change date. If the value is 0, the user will be forced to change the password at the next login. See chage command in Linux with examples and 10 chage command examples in Linux.
NEW QUESTION # 154
A Linux administrator rebooted a server. Users then reported some of their files were missing. After doing some troubleshooting, the administrator found one of the filesystems was missing. The filesystem was not listed in /etc/f stab and might have been mounted manually by someone prior to reboot. Which of the following would prevent this issue from reoccurring in the future?
- A. Sync the mount units.
- B. Mount the filesystem manually.
- C. Create a mount unit and enable it to be started at boot.
- D. Remount all the missing filesystems
Answer: C
Explanation:
The best way to prevent this issue from reoccurring in the future is to create a mount unit and enable it to be started at boot. A mount unit is a systemd unit that defines how and where a filesystem should be mounted.
By creating a mount unit for the missing filesystem and enabling it with systemct1 enable, the administrator can ensure that the filesystem will be automatically mounted at boot time, regardless of whether it is listed in
/etc/fstab or not. Syncing the mount units will not prevent the issue, as it will only synchronize the state of existing mount units with /etc/fstab, not create new ones. Mounting the filesystem manually will not prevent the issue, as it will only mount the filesystem temporarily, not permanently. Remounting all the missing filesystems will not prevent the issue, as it will only mount the filesystems until the next reboot, not after. References: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 14: Managing Disk Storage, page 457.
NEW QUESTION # 155
A Linux system is getting an error indicating the root filesystem is full. Which of the following commands should be used by the systems administrator to resolve this issue? (Choose three.)
- A. parted -l /dev/mapper/rootvg-rootlv
- B. growpart /dev/mapper/rootvg-rootlv
- C. lvresize -L +10G -r /dev/mapper/rootvg-rootlv
- D. df -h /
- E. vgextend /dev/rootvg /dev/sdb
- F. pvcreate /dev/sdb
- G. lsblk /dev/sda
- H. fdisk -1 /dev/sdb
Answer: B,C,D
Explanation:
The administrator should use the following three commands to resolve the issue of the root filesystem being full:
df -h /. This command will show the disk usage of the root filesystem in a human-readable format. The df command is a tool for reporting file system disk space usage. The -h option displays the sizes in powers of 1024 (e.g., 1K, 234M, 2G). The / specifies the root filesystem. The command df -h / will show the total size, used space, available space, and percentage of the root filesystem. This command will help the administrator identify the problem and plan the solution.
growpart /dev/mapper/rootvg-rootlv. This command will grow the partition that contains the root filesystem to the maximum size available. The growpart command is a tool for resizing partitions on Linux systems. The /dev/mapper/rootvg-rootlv is the device name of the partition, which is a logical volume managed by the Logical Volume Manager (LVM). The command growpart /dev/mapper/rootvg-rootlv will extend the partition to fill the disk space and increase the size of the root filesystem. This command will help the administrator solve the problem and free up space.
lvresize -L +10G -r /dev/mapper/rootvg-rootlv. This command will resize the logical volume that contains the root filesystem and add 10 GB of space. The lvresize command is a tool for resizing logical volumes on Linux systems. The -L option specifies the new size of the logical volume, in this case +10G, which means 10 GB more than the current size. The -r option resizes the underlying file system as well. The /dev/mapper/rootvg-rootlv is the device name of the logical volume, which is the same as the partition name. The command lvresize -L +10G -r /dev/mapper/rootvg-rootlv will increase the size of the logical volume and the root filesystem by 10 GB and free up space. This command will help the administrator solve the problem and free up space.
The other options are incorrect because they either do not affect the root filesystem (fdisk -1 /dev/sdb, pvcreate /dev/sdb, lsblk /dev/sda, or vgextend /dev/rootvg /dev/sdb) or do not use the correct syntax (fdisk -1 /dev/sdb instead of fdisk -l /dev/sdb or parted -l /dev/mapper/rootvg-rootlv instead of parted /dev/mapper/rootvg-rootlv print). Reference: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 10: Managing Storage, pages 318-319, 331-332.
NEW QUESTION # 156
A Linux administrator needs to expose port 9000 for a container to listen during runtime. The Linux administrator creates a Dockerfile with the following entries:
sql
FROM node:9-alpine
WORKDIR /usr/src/app
COPY package.json ./
RUN npm install
COPY . .
EXPOSE 9000
CMD ["npm", "start"]
Which of the following commands should the administrator use to accomplish this task? (Select two).
- A. docker run -p 80:9000 Test-Container
- B. docker push Test-Container
- C. docker inspect Test-Container
- D. docker build -t Test-Container
- E. docker run -p 5000:80 Test-Container
- F. docker tag Test-Container
Answer: A,D
Explanation:
First, the administrator should build the container image using the command docker build -t Test-Container, which creates a Docker image with the specified configuration. To run the container and expose port 9000, the correct command is docker run -p 80:9000 Test-Container, which maps the container's port 9000 to port
80 on the host machine, making the service accessible externally on port 80.
NEW QUESTION # 157
An administrator is using a configuration management tool to define a system's configuration. The defined configuration can be used to provision new systems, rebuild existing systems, or roll back systems to their original baseline configurations.
Which of the following BEST describes what the administrator is doing?
- A. Test automation
- B. Containerization
- C. Build automation
- D. Infrastructure as code
Answer: A
NEW QUESTION # 158
An administrator attempts to rename a file on a server but receives the following error.
The administrator then runs a few commands and obtains the following output:
Which of the following commands should the administrator run NEXT to allow the file to be renamed by any user?
- A. chacl -R 644 files
- B. chmod -t files
- C. chown users files
- D. chgrp reet files
Answer: B
Explanation:
The command that the administrator should run NEXT to allow the file to be renamed by any user is chmod -t files. This command uses the chmod tool, which is used to change file permissions and access modes. The -t option removes (or sets) the sticky bit on a directory, which restricts deletion or renaming of files within that directory to only their owners or root. In this case, since files is a directory with sticky bit set (indicated by t in drwxrwxrwt), removing it will allow any user to rename or delete files within that directory.
The other options are not correct commands for allowing any user to rename files within files directory. The chgrp reet files command will change the group ownership of files directory to reet, but it will not affect its permissions or access modes. The chacl -R 644 files command is invalid, as chacl is used to change file access control lists (ACLs), not permissions or access modes. The chown users files command will change the user ownership of files directory to users, but it will not affect its permissions or access modes. References: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 8: Managing Users and Groups; chmod(1) - Linux manual page
NEW QUESTION # 159
Joe, a user, is unable to log in to the Linux system Given the following output:
Which of the following command would resolve the issue?
- A. passwd -u joe
- B. usermod -s /bin/bash joe
- C. chage -E 90 joe
- D. pam_tally2 -u joe -r
Answer: D
Explanation:
Based on the output of the image sent by the user, Joe is unable to log in to the Linux system because his account has been locked due to too many failed login attempts. The pam_tally2 -u joe -r command will resolve this issue by resetting Joe's failed login counter to zero and unlocking his account. This command uses the pam_tally2 module to manage user account locking based on login failures. The usermod -s /bin/bash joe command will change Joe's login shell to /bin/bash, but this will not unlock his account. The passwd -u joe command will unlock Joe's password if it has been locked by passwd -l joe, but this will not reset his failed login counter or unlock his account if it has been locked by pam_tally2. The chage -E 90 joe command will set Joe's account expiration date to 90 days from today, but this will not unlock his account or reset his failed login counter. References: CompTIA Linux+ (XK0-005) Certification Study Guide, Chapter 18:
Securing Linux Systems, page 537.
NEW QUESTION # 160
......
2026 New Preparation Guide of CompTIA XK0-005 Exam: https://www.examstorrent.com/XK0-005-exam-dumps-torrent.html
XK0-005 Practice Exam - 895 Unique Questions: https://drive.google.com/open?id=1CwF01ZZqwEPupA3Xo1iO4zK6K3aSu8nX